Clean up resources
You would clean up resources in the following order:
Delete S3 bucket
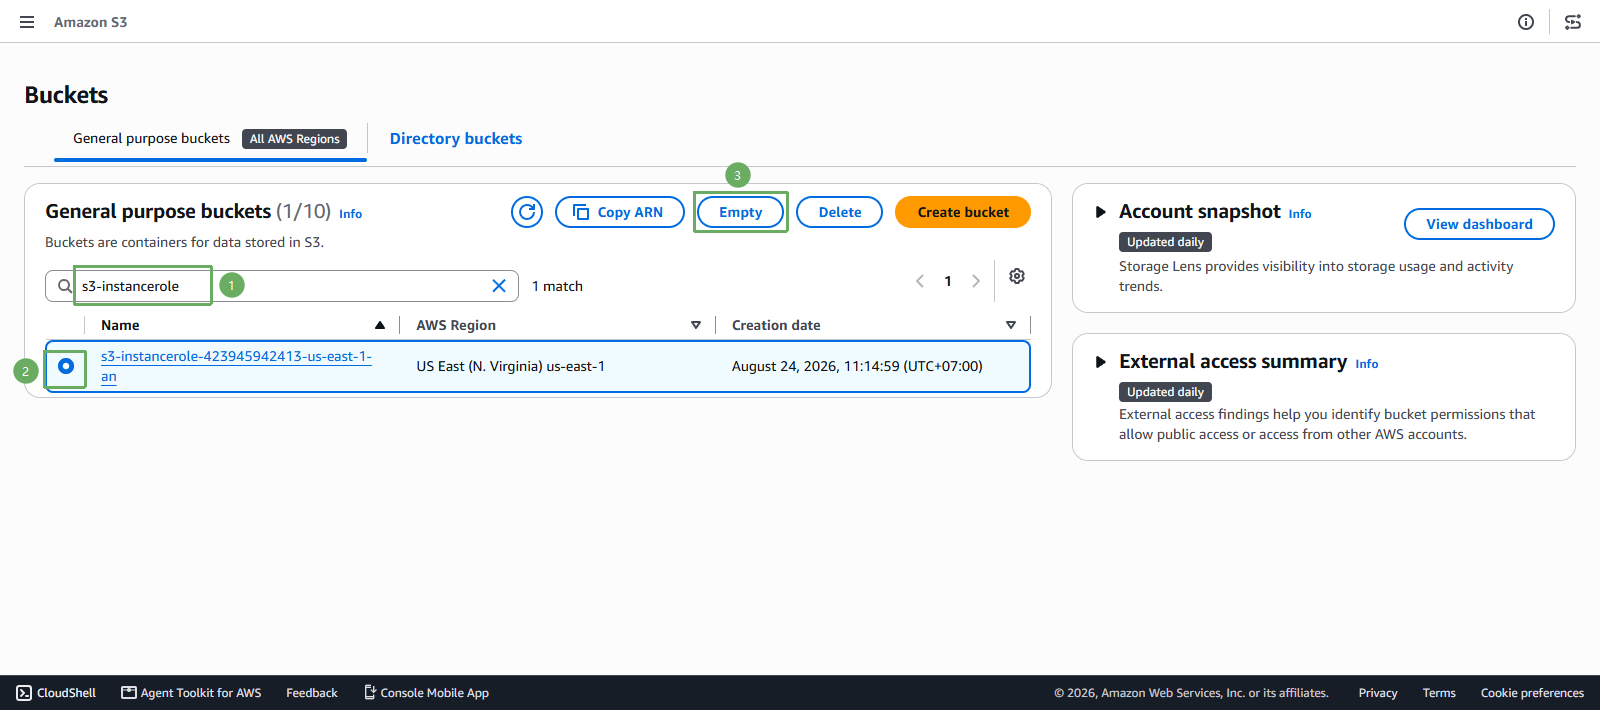
- Click on S3 bucket s3-instancerole-xxxx.
- Click Empty.
- Enter
permanently deleteto confirm, then click Empty to delete all data in S3 bucket.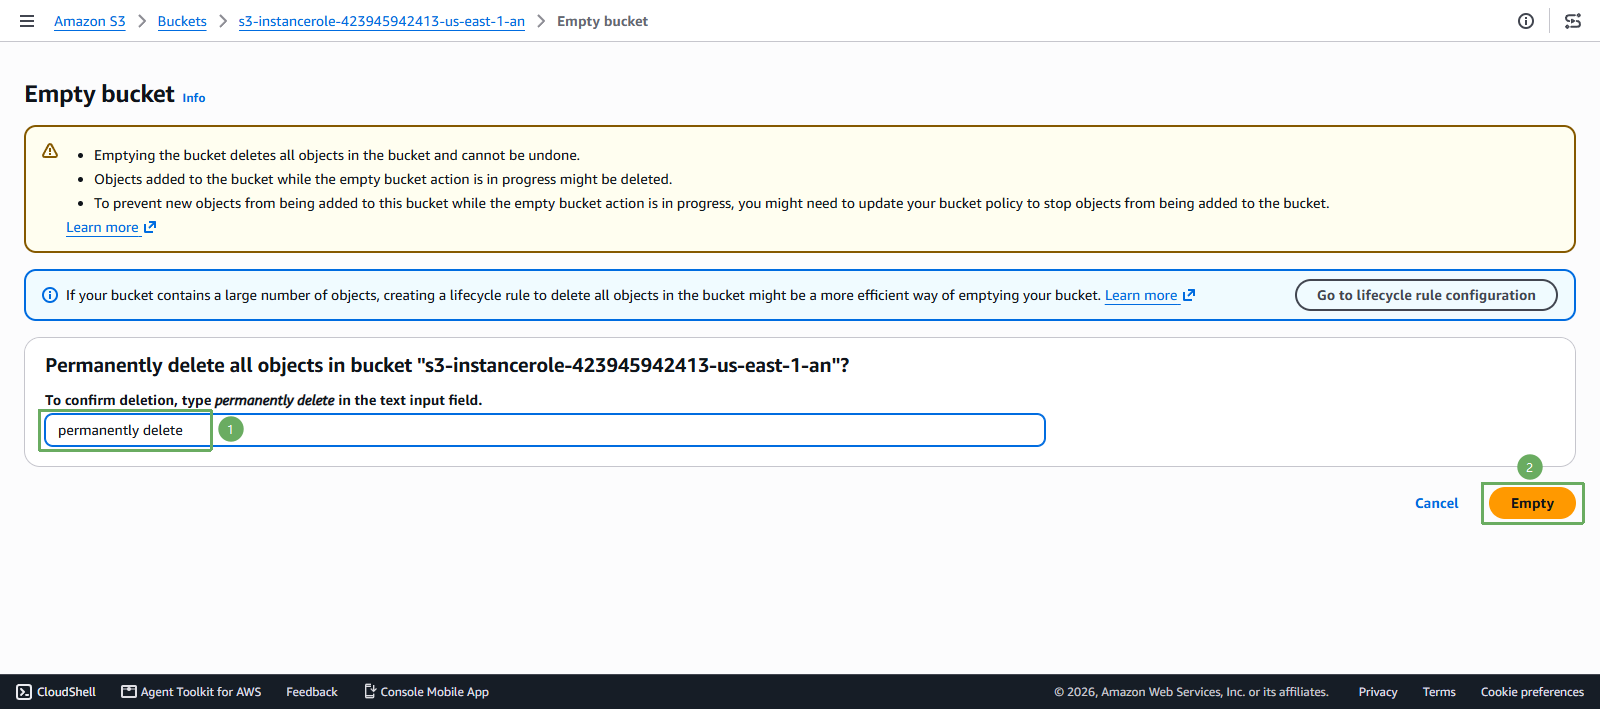
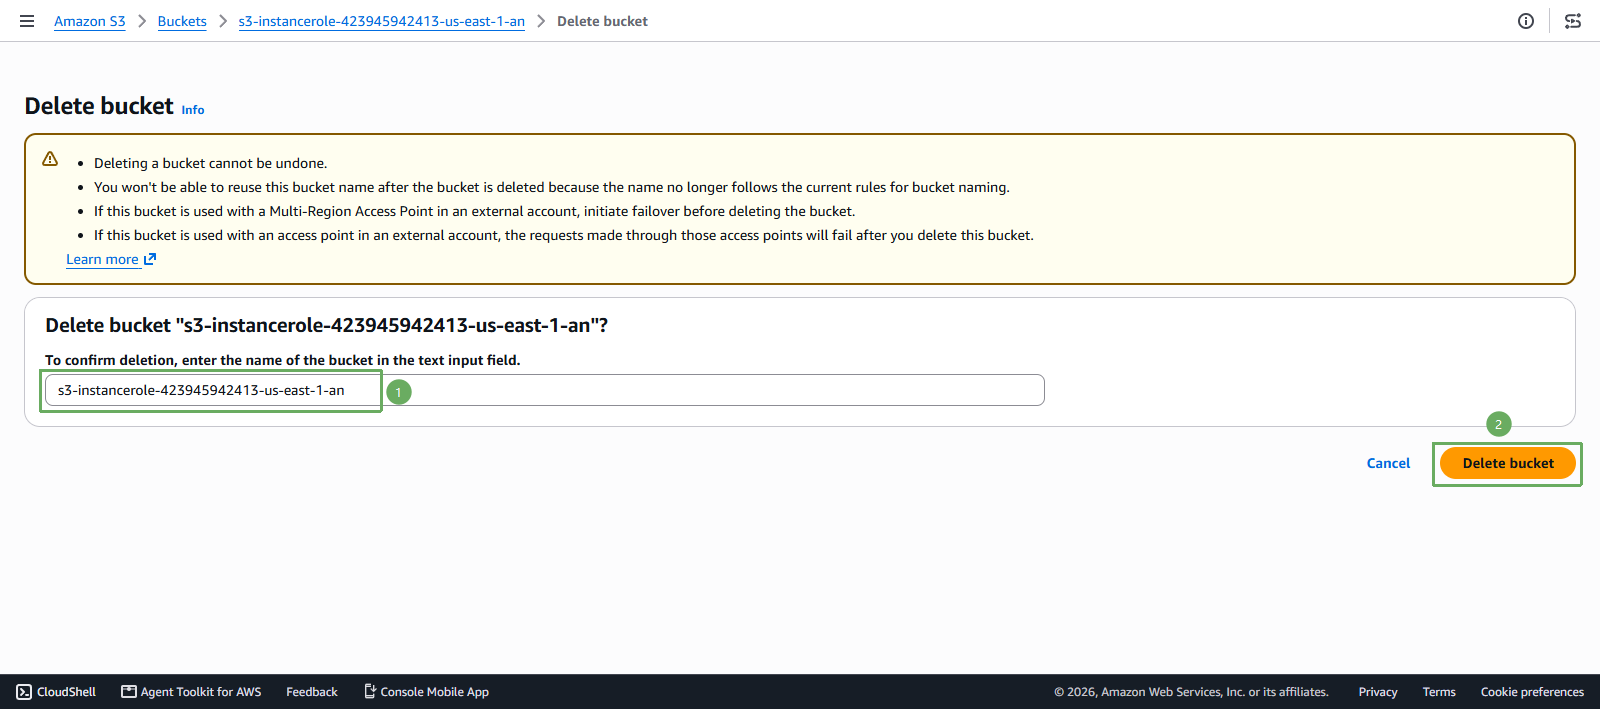
- Click the S3 bucket s3-instancerole-xxxx, then click Delete.
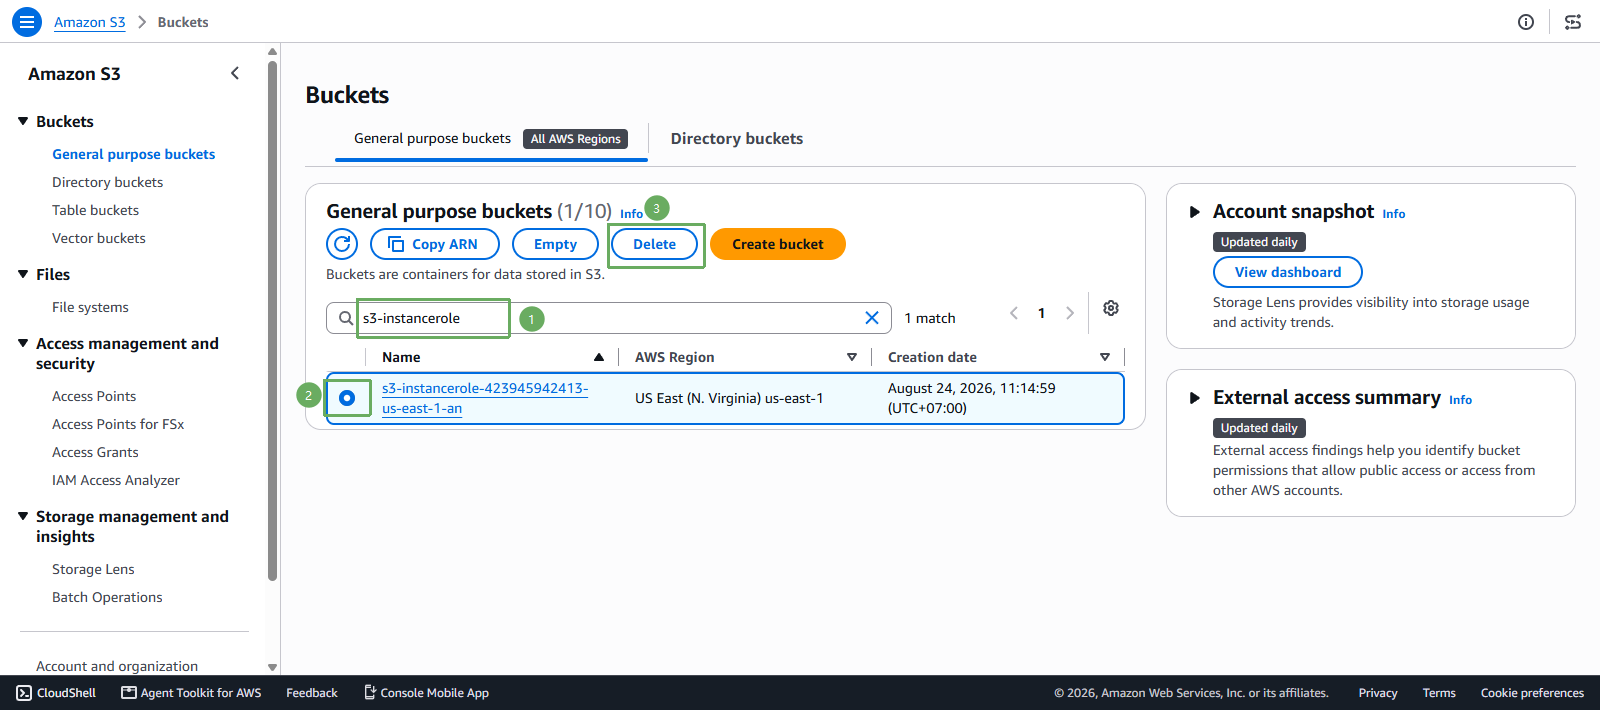
- Enter the bucket name then click Delete bucket to delete the S3 bucket.
Delete EC2 Instance
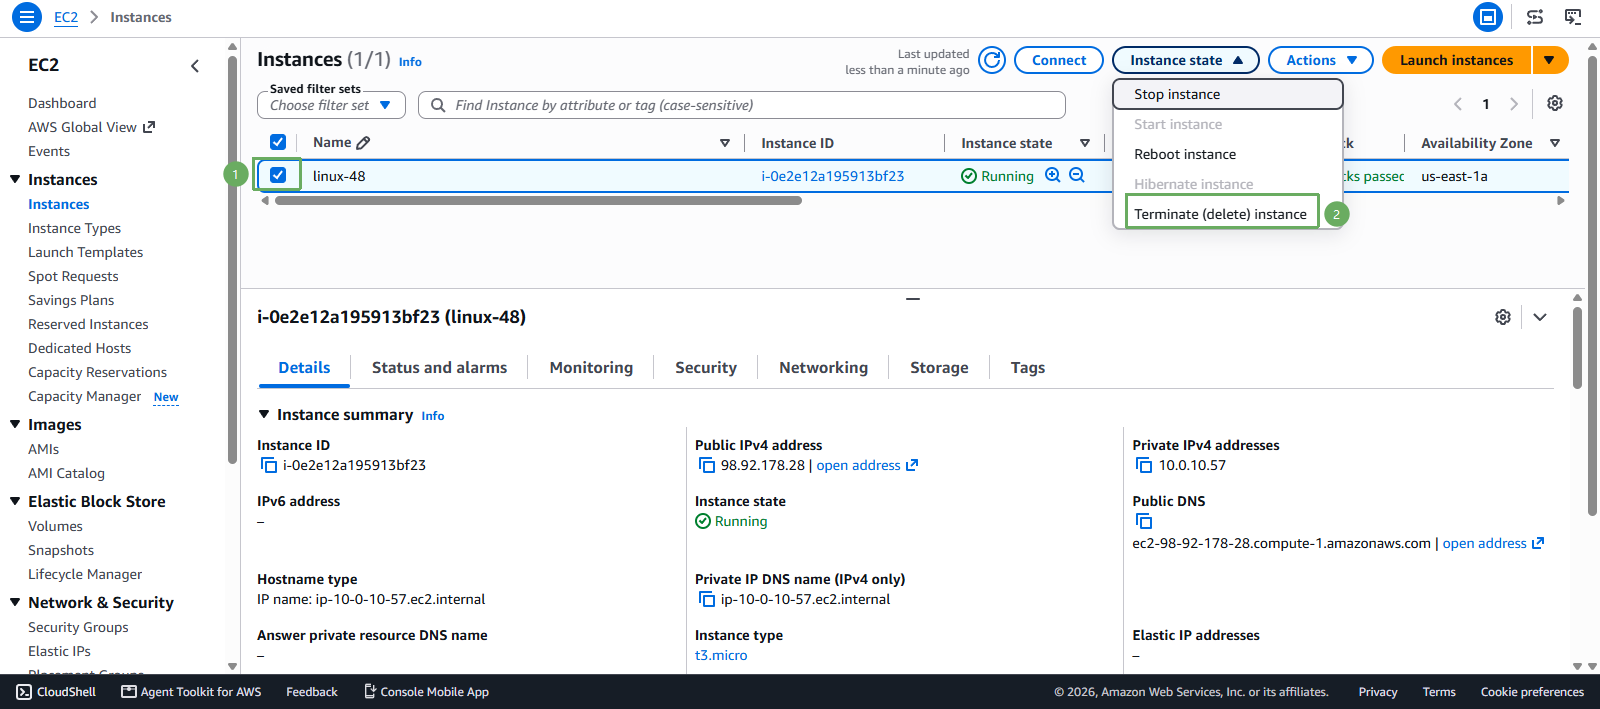
- Click on the Instance we created for the lab.
- Click Instance state.
- Click Terminate instance , then click Terminate to confirm.
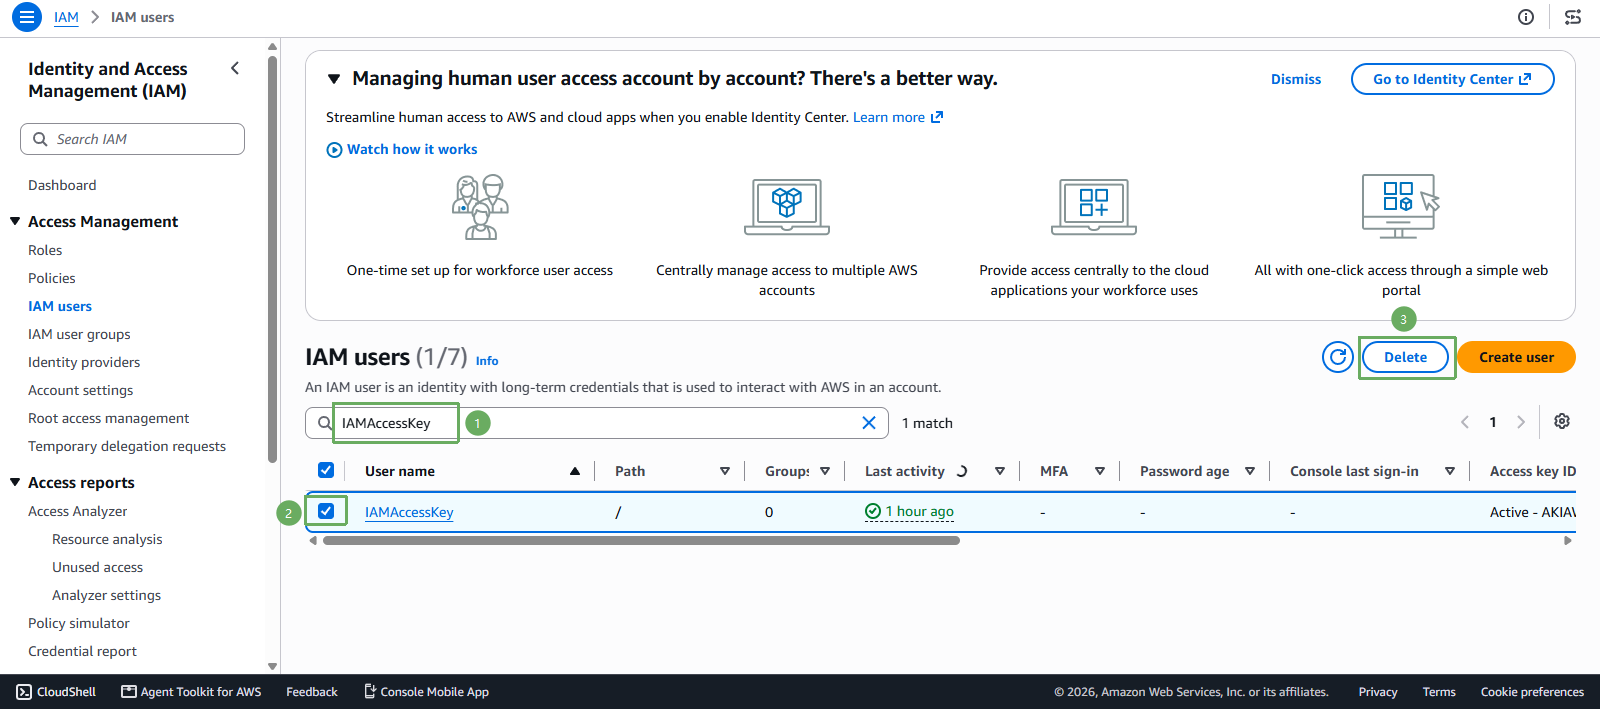
- Click Users
- Click on user IAMAccessKey.
- Click Delete.
- Choose Deactive access key
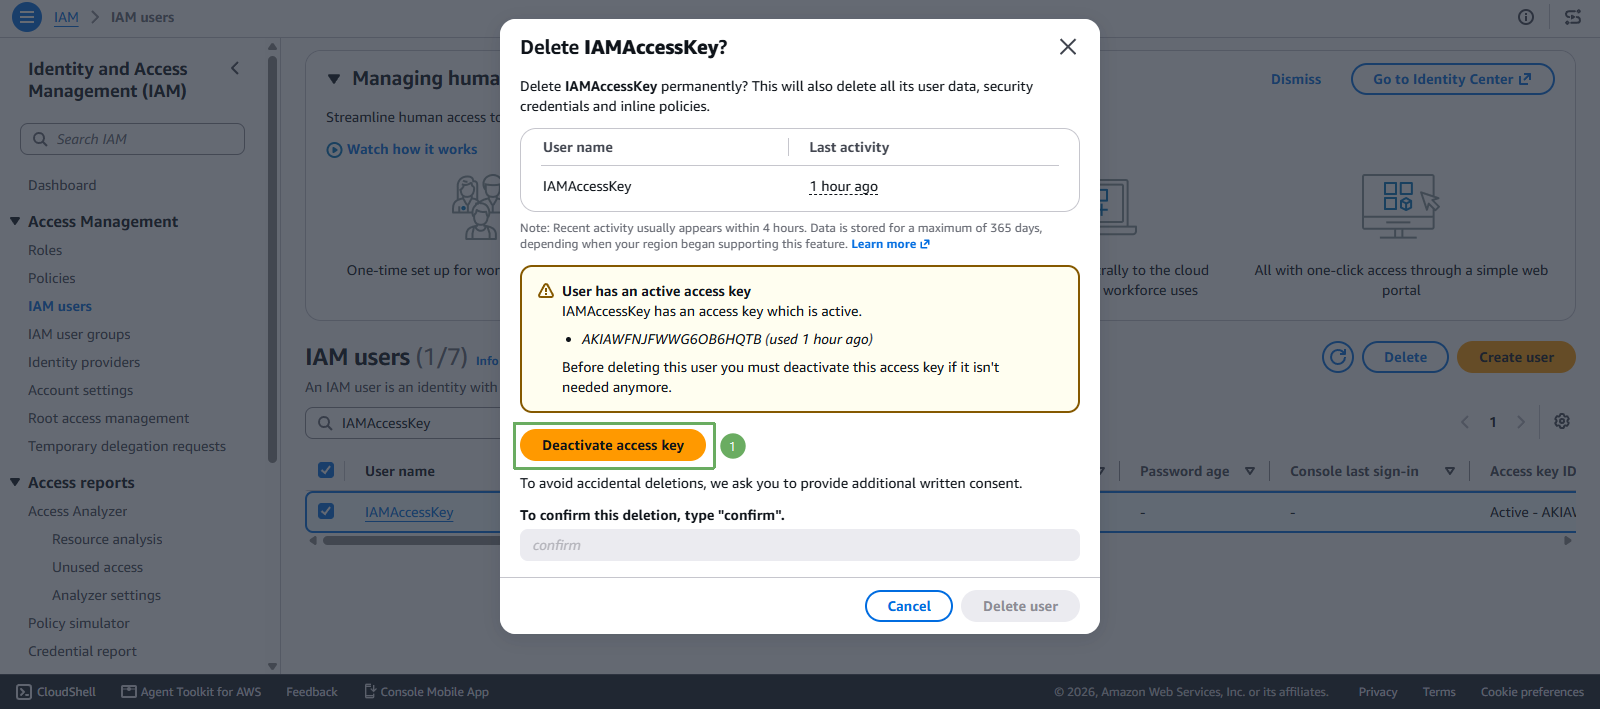
- Type
confirmand click Delete user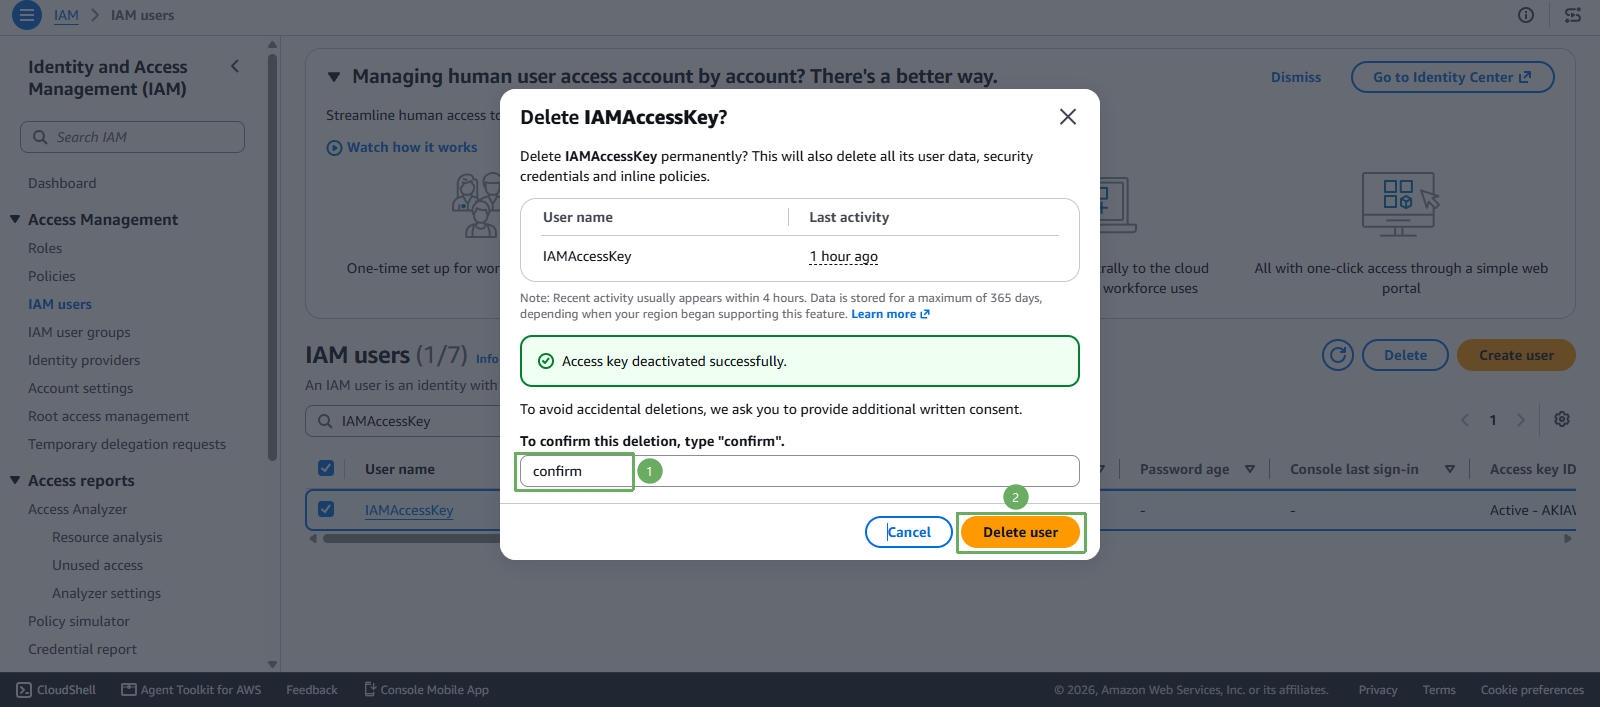
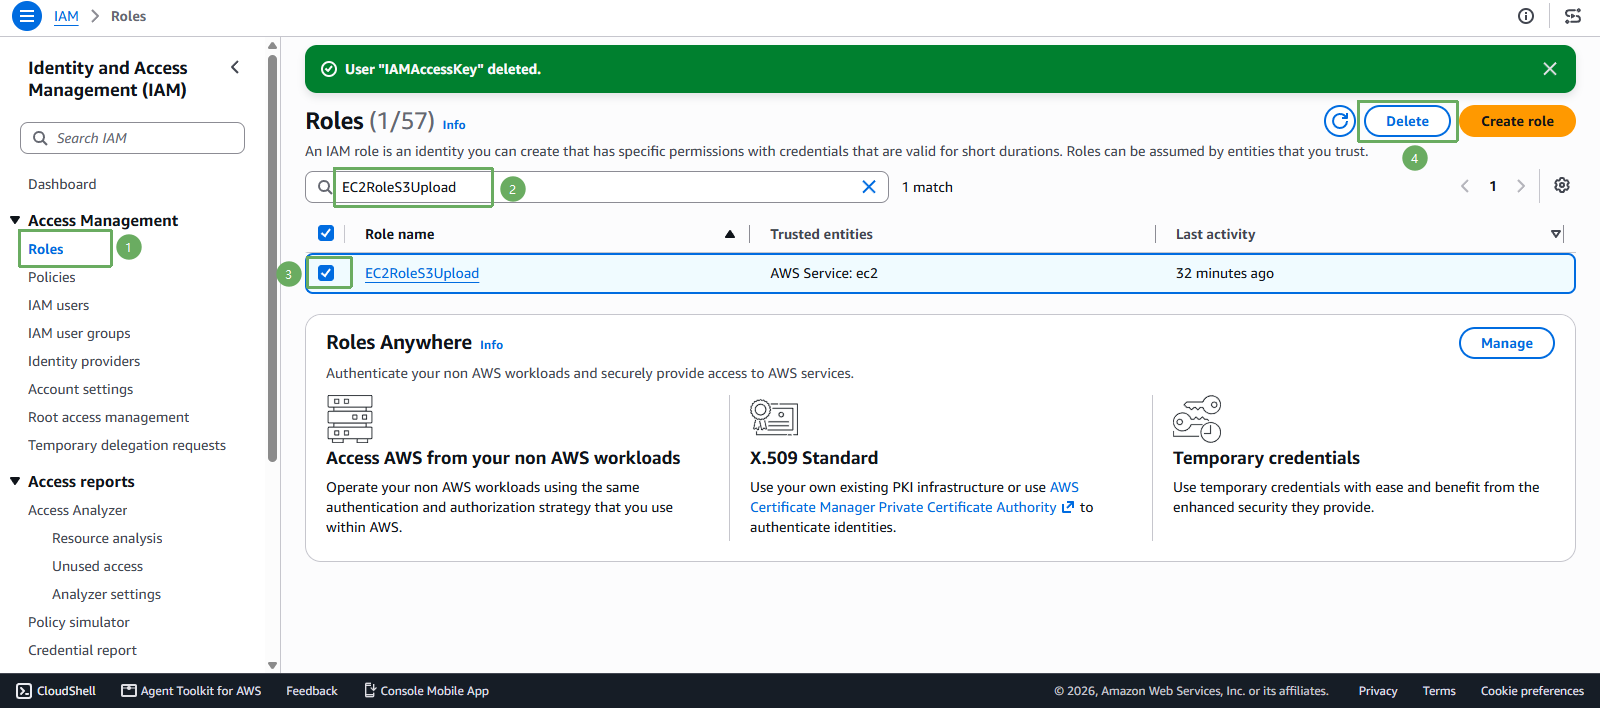
- Click Roles tab.
- Enter ec2 to find the role we created.
- Click on role EC2RoleS3Upload.
- Click Delete. Enter the role name EC2RoleS3Upload and click Delete to delete the IAM Role.