Create IAM role
Create IAM role
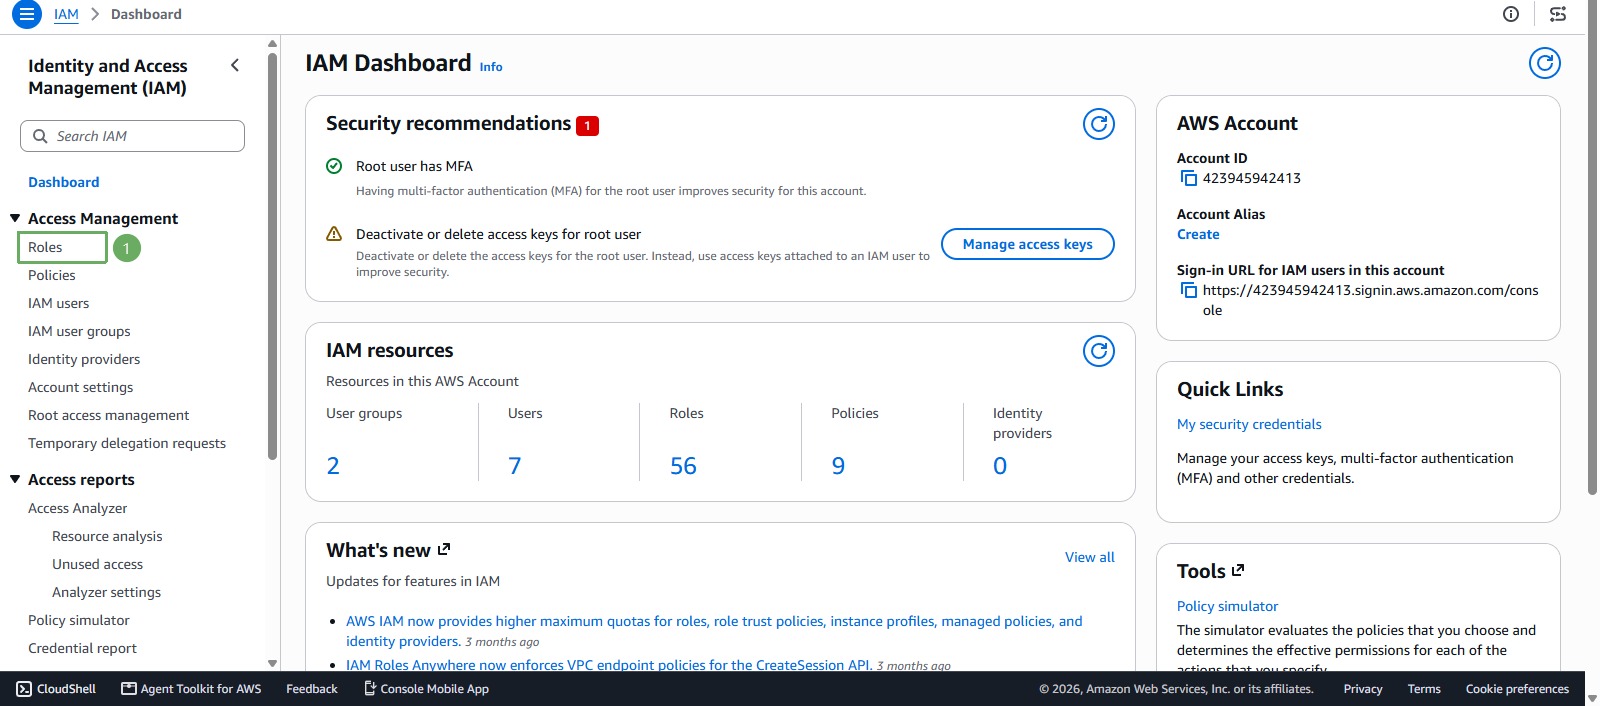
- Click Roles.
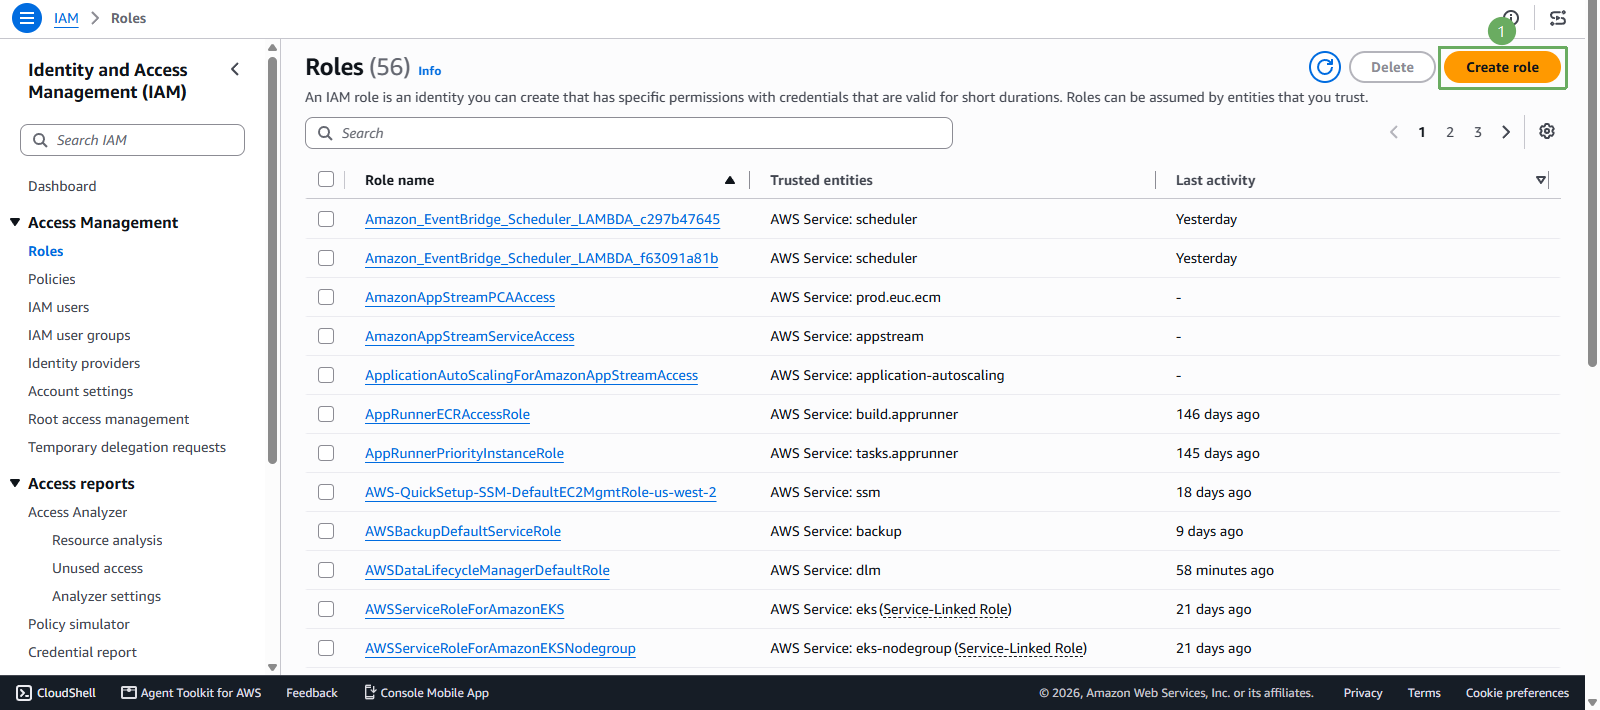
- Click Create role
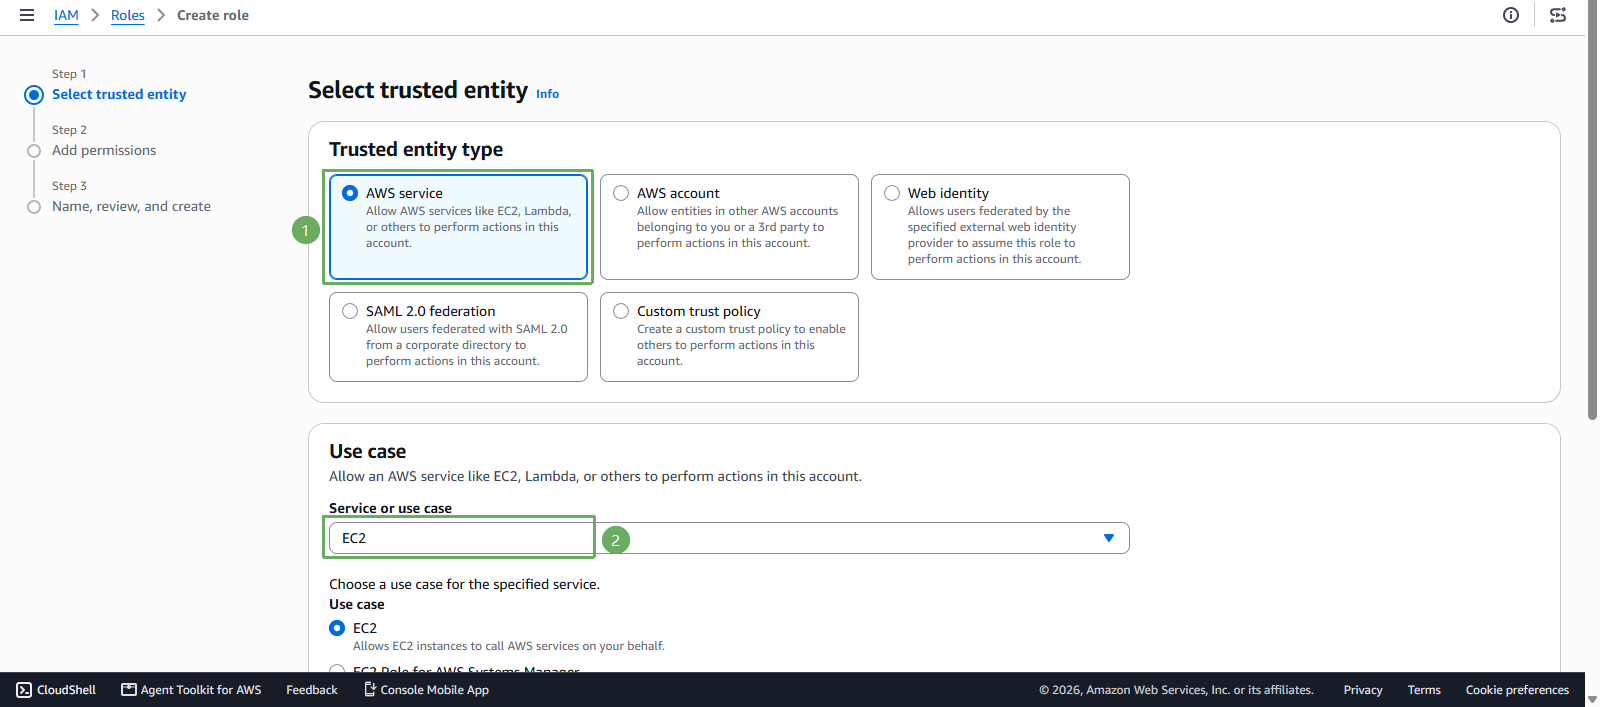
- In the Select trusted identity section:
- Click on AWS service.
- Service or use case: EC2 to create an IAM role to use for the application running inside EC2 instance.
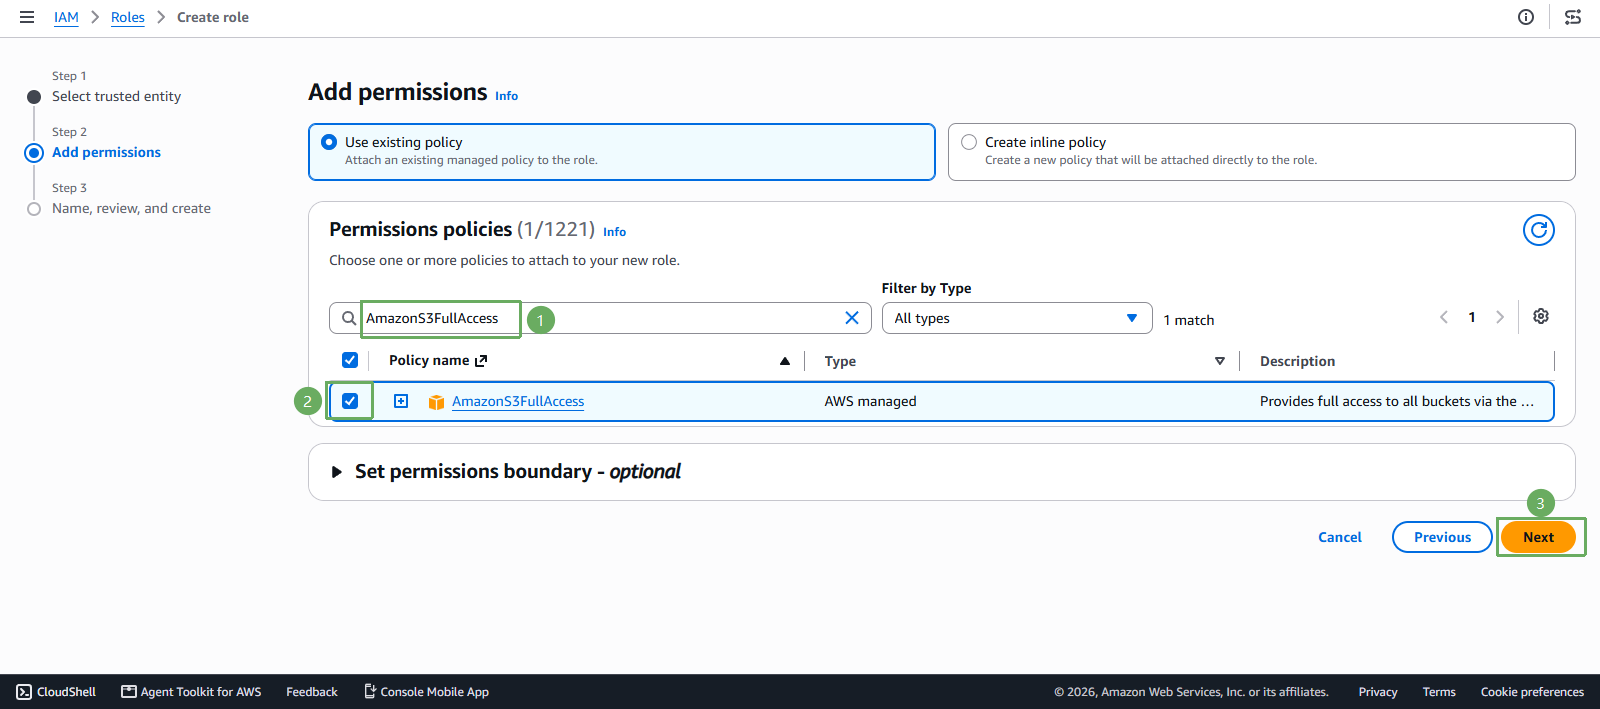
- In the Policy name box, enter AmazonS3FullAccess.
- Click AmazonS3FullAccess, we will grant full access to access and upload files to the S3 bucket we created.
- Click Next.
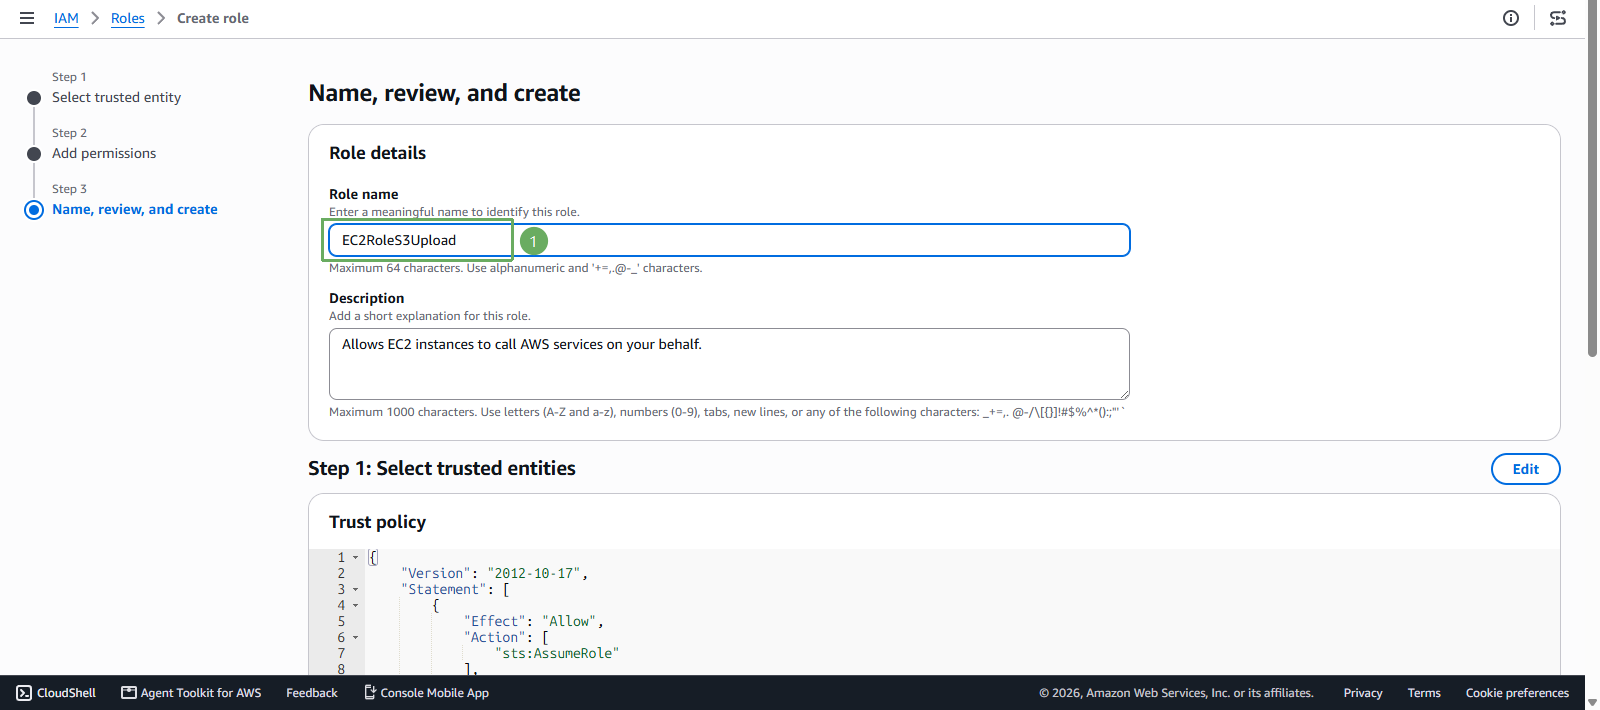
- Set Role name to
EC2RoleS3Upload. Click Create role.
Next, we will use this role to assign to the EC2 instance and make it possible for our application to upload files to S3 without using the access key and secret access key in the code.